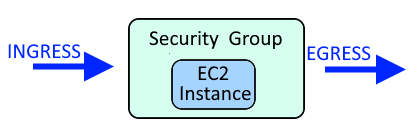
A Security Group is used to allow or deny requests coming in (ingress) and/or requests going out (egress). For example, a Security Group could be used to only allow requests within a certain IP address range to come in (ingress) and go out (egress) of an EC2 Instance.
This assumes you have already configured the aws command line tool. If not, check out my article on Getting Started with the AWS CLI.
The aws ec2 describe-security-group command can be used to list your EC2 security groups.
aws ec2 describe-security-groups
Something like this should be returned.
{
    "SecurityGroups": [
        {
            "Description": "My security group",
            "IpPermissions": [
                {
                    "FromPort": 22,
                    "IpProtocol": "tcp",
                    "IpRanges": [
                        {
                            "CidrIp": "0.0.0.0/0",
                            "Description": "SSH"
                        }
                    ],
                    "Ipv6Ranges": [],
                    "PrefixListIds": [],
                    "ToPort": 22,
                    "UserIdGroupPairs": []
                }
            ],

            "IpPermissionsEgress": [
                {
                    "IpProtocol": "-1",
                    "IpRanges": [
                        {
                            "CidrIp": "0.0.0.0/0"
                        }
                    ],
                    "UserIdGroupPairs": [],
                    "PrefixListIds": []
                }
            ],
            "Tags": [
                {
                    "Value": "my Security Group",
                    "Key": "Name"
                }
            ],
            "GroupName": "MySecurityGroup",
            "VpcId": "vpc-1a2b34aa",
            "OwnerId": "123456789012",
            "GroupId": "sg-90334aa8",
        }
    ]
}
The aws ec2 describe-security-group-rules command can be used to list the inbound and outbound rules associated with a EC2 security groups.
aws ec2 describe-security-group-rules
--filter can be used to match a specific Security Group.
aws ec2 describe-security-group-rules --filter Name="group-id",Values="sg-1234567890abcdef0"
Something like this should be returned.
{
    "SecurityGroupRules": [
        {
            "SecurityGroupRuleId": "sgr-05ee7f82c0ae7578f",
            "GroupId": "sg-0778124087b3d14d4",
            "GroupOwnerId": "123456789012",
            "IsEgress": false,
            "IpProtocol": "tcp",
            "FromPort": 22,
            "ToPort": 22,
            "CidrIpv4": "0.0.0.0/0",
            "Description": "Allow SSH from All",
            "Tags": []
        },
        {
            "SecurityGroupRuleId": "sgr-05eeabdcc0ae1234f",
            "GroupId": "sg-0778124087b3d14d4",
            "GroupOwnerId": "123456789012",
            "IsEgress": false,
            "IpProtocol": "tcp",
            "FromPort": 80,
            "ToPort": 80,
            "CidrIpv4": "0.0.0.0/0",
            "Description": "Allow HTTP from All",
            "Tags": []
        }
    ]
}
Did you find this article helpful?
If so, consider buying me a coffee over at